


Knowledge Base
Domain Validation Reuse Changes in 2027
Important: DigiCert may update this article if new information becomes available. Save this page and check for updates. The Last Modified date appears under the title. |
On March 1, 2027, DigiCert will shorten the domain validation reuse period from 199 days to 99 days. The domain validation reuse period is how long a certificate authority (CA) can use a completed domain validation to issue certificates before you need to validate the domain again. The shorter reuse period is required by CA/Browser Forum Ballot SC081v3, which reduces the maximum domain validation reuse period from 200 days to 100 days. DigiCert sets its reuse period 1 day shorter than the CA/Browser Forum maximum to make sure it never exceeds the permitted limit.
The shorter reuse period affects all certificates that use the CA/Browser Forum TLS Baseline Requirements for domain validation, including public OV and EV TLS, EU Qualified Website Authentication Certificate (QWAC), EU QWAC PSD2, Secure Email for Employee, and Secure Email for Organization. It applies to every domain control validation (DCV) method except Persistent DNS TXT Record.
No immediate action is required. However, this change also applies to existing domain validations, so some validations completed before March 1, 2027, may expire sooner than they would under the 199-day reuse period. If you validate domains manually, prepare to revalidate them more often. See What's changing for how the change affects your existing domain validations.
Note: This change does not affect:
|
In this article
- What's changing
- Does this change affect me?
- What do I need to do?
- Prevent expired domain validations from delaying certificate issuance
- Why is DigiCert doing this?
What's changing
Starting March 1, 2027, the 99-day reuse period applies to both new and existing domain validations. CA/Browser Forum Ballot SC081v3 requires CAs to apply the new limit to existing domain validations, so a domain validation completed before March 1, 2027, may expire sooner than it would under the 199-day reuse period in place until March 1, 2027. Use Table 1 to see how the change affects your existing domain validations.
Table 1: How the 99-day reuse period affects your domain validations
| If your domain was validated... | Domain validation reuse as of March 1, 2027 |
| On or before August 14, 2026 | No change. These validations already expire on or before March 1, 2027, under the 199-day reuse period. |
| Between August 15, 2026, and November 22, 2026 | Reuse is shortened so that these validations expire on March 1, 2027. |
| Between November 23, 2026, and February 28, 2027 | Reuse is shortened to 99 days from the validation date. These validations expire earlier than they would under the 199-day reuse period. |
| On or after March 1, 2027 | These validations can be reused for up to 99 days. |
Does this change affect me?
If you use DigiCert certificates that allow you to reuse domain validations, the 99-day domain validation reuse period that starts on March 1, 2027, may affect you. Use Table 2 to check both the certificates you use and how you validate your domains.
Table 2: How the 99-day reuse period affects you
| If you... | Impact |
| Use public OV TLS, EV TLS, QWAC, QWAC PSD2, Secure Email for Employee, or Secure Email for Organization certificates | Domain validations expire after 99 days instead of 199 days. |
| Use public DV TLS certificates | No impact. DigiCert DV certificates do not support domain validation reuse. |
| Validate domains manually | You need to revalidate domains more often. To reduce manual work, see Prevent expired domain validations from delaying certificate issuance. |
| Automate domain validation | Minimal impact. Verify that your automated process continues to revalidate domains before their validations expire. |
| Use Persistent DNS TXT Record validation | No impact. Domain validations using this method can already be reused for a maximum of 9 days at DigiCert, and CertCentral revalidates them automatically. |
What do I need to do?
No immediate action is required. However, if you validate your domains manually, DigiCert recommends preparing now for domain validations to expire after 99 days beginning March 1, 2027.
Plan for March 1, 2027, in particular. All domain validations completed between August 15, 2026, and November 22, 2026, expire on that date, so you may need to revalidate several domains at once. To avoid delays, check your domain validation expiration dates and revalidate domains before they expire.
What happens if my domain validation expires?
When your domain validation expires, you must revalidate your domain before DigiCert can issue your certificate. This may delay certificate issuance for new, renewal, and reissue requests.
For OV and EV TLS certificates, expired domain validation also prevents you from requesting duplicate certificates. Duplicate certificates are designed for immediate issuance and do not support completing domain or organization validation after the request has been submitted.
How to check domain validation expiration dates
- In CertCentral, go to the domains page.
- Enterprise, Partner, and legacy accounts: In the left menu, go to Certificates > Domains.
- Subscription accounts: In the left menu, go to Validation > Domains.
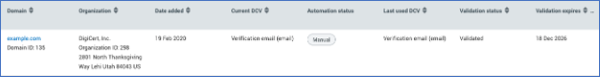
- On the Domains page, in the Automation status column, check whether your domain validation is automated.
- In the Validation expires column, check when you need to revalidate the domain.
- To revalidate a domain before its validation expires, see Revalidate a domain before its validation expires.
Prevent expired domain validations from delaying certificate issuance
Automation keeps your domain validations current, so expired validations don't delay certificate issuance. If you use CertCentral, see Option 1 or the CertCentral options in Option 2. If you use Trust Lifecycle Manager, see the Trust Lifecycle Manager options in Option 2.
Option 1: Automate domain validation
Automate DCV with UltraDNS
If your DNS is hosted with UltraDNS, connect it to CertCentral to automate domain validation.
- CertCentral automatically adds a DNS TXT record in UltraDNS with the DigiCert-generated random value required for DNS TXT validation, then removes the record once validation completes.
- CertCentral repeats this process every 7 days.
Learn how to automate your CertCentral domain validation with UltraDNS.
Automate DCV with Persistent DNS TXT Record
Persistent DNS TXT Record isn't affected by the 99-day reuse period. Validations using this method can be reused for 9 days, and CertCentral revalidates domains using this method automatically. You only need to validate each domain manually once.
- After the first validation, CertCentral revalidates the domain using the persistent TXT record already in place. You don't need to resubmit anything.
- CertCentral revalidates the domain every 5 days.
Learn how to add and validate a domain using Persistent DNS TXT record.
Related: Bulk domain revalidation support for the Persistent DNS TXT record method and CertCentral: Persistent DNS TXT automatic domain revalidation
Option 2: Automate certificate management
Use an automated certificate management solution that handles domain validation as part of the certificate lifecycle.
CertCentral automation
- Enterprise, Partner, and legacy accounts: Use any compliant ACME client to manage the certificates installed on your servers. Learn about CertCentral ACME automation service.
- Subscription accounts: Use the CertCentral automation agent to manage the certificates installed on your servers. Learn about the CertCentral automation agent.
Trust Lifecycle Manager ACME
Use any compliant ACME client with the Trust Lifecycle Manager ACME service to manage the certificates installed on your servers. Learn about Trust Lifecycle Manager ACME automation service.
Trust Lifecycle Manager managed automation
Automate certificates on servers, network appliances, cloud services, and vaults, and manage all your certificate deployments in one place from the Trust Lifecycle Manager web console or REST API. Learn about Trust Lifecycle Manager managed automation.
Why is DigiCert doing this?
DigiCert is shortening the domain validation reuse period to 99 days on March 1, 2027, to comply with CA/Browser Forum Ballot SC081v3, an industry standard that reduces the maximum amount of time CAs can reuse domain validation information. This ballot sets a phased timeline to reduce the maximum domain validation reuse period to 100 days on March 15, 2027, and to 10 days on March 15, 2029. DigiCert sets its maximum validation reuse period 1 day shorter than the CA/Browser Forum’s allowed maximum to ensure DigiCert does not exceed the permitted reuse window.
Learn more about Ballot SC081v3.
Table 3: Domain validation reuse timeline
| CA/Browser Forum maximum reuse period | CA/Browser Forum effective dates | DigiCert maximum reuse period | DigiCert timeline |
| 200 days | Between March 15, 2026, and March 15, 2027 | 199 days | Between February 24, 2026, and March 1, 2027 |
| 100 days | Between March 15, 2027, and March 15, 2029 | 99 days | From March 1, 2027, until DigiCert moves to a 9-day reuse period |
| 10 days | As of March 15, 2029 | 9 days | No later than March 15, 2029 |
-
The most-trusted global provider of high-assurance TLS/SSL, PKI, IoT and signing solutions.
-


-
© 2022-2026, DigiCert, Inc. All rights reserved.
Cookie Settings
